SIEM Monitored 24x7 by a SOC: Essential Protection for Indian Healthcare
Comparing siem monitored 24x7 by a soc Models for Healthcare Security
Healthcare organizations increasingly depend on connected applications, digital records, clinical systems, networks, endpoints, and online services. As technology expands, so does the need to identify suspicious activity quickly. siem monitored 24x7 by a soc combines security information and event management with continuous security operations, giving healthcare IT teams a structured way to monitor security activity throughout the day and night.
For Indian healthcare organizations, the important question is not simply whether they have a SIEM or SOC. It is whether their chosen operating model provides appropriate visibility, qualified analysis, clear escalation, and dependable security processes.
What Is siem monitored 24x7 by a soc in Healthcare?
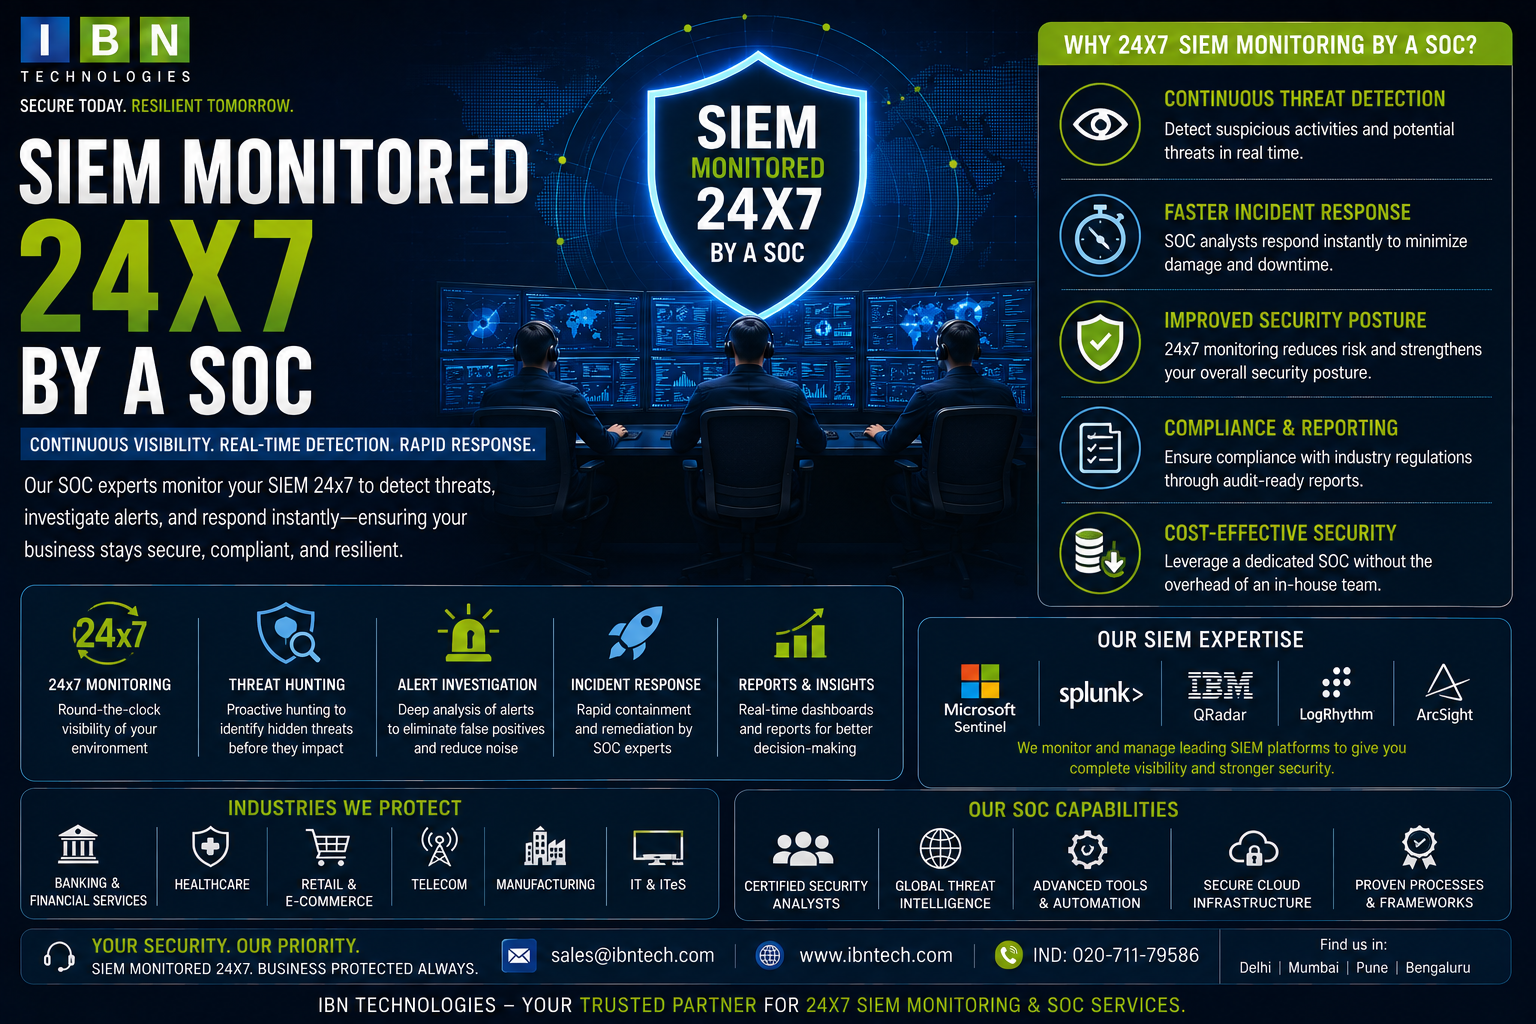
SIEM monitored 24×7 by a SOC means security events from supported healthcare technology environments are collected and analyzed through SIEM capabilities while security professionals continuously monitor relevant alerts through a security operations center.
The model connects security technology with human investigation. Instead of depending entirely on automated alerts or occasional reviews, organizations can establish an ongoing process for identifying and assessing potentially suspicious activity.
How soc as a service companies Fit Into Healthcare Security
Healthcare organizations have different technology environments and internal security capabilities. soc as a service companies can provide an external operating model for organizations that need continuous security monitoring without developing every SOC function internally.
The value of this approach depends on the actual service scope. Healthcare leaders should understand which systems are monitored, how alerts are investigated, how incidents are escalated, and what responsibilities remain with the organization's internal IT and security teams.
This makes service evaluation more important than simply selecting an external provider based on the availability of 24×7 monitoring.
Three Common Approaches to Security Monitoring
Healthcare organizations can generally approach continuous security operations in different ways.
Internal Security Operations
An organization can build and operate its own SOC using internal personnel and technology. This can provide direct control over processes, security architecture, and operational priorities.
However, an internal model requires the organization to manage staffing, skills, monitoring procedures, technology administration, alert investigation, and continuous operational coverage.
Co-Managed Security Operations
A co-managed model combines internal security personnel with external SOC capabilities. Internal teams retain responsibility for selected activities while an external security operation supports monitoring or specific operational functions.
This can be useful when a healthcare organization already has security expertise but requires additional monitoring capacity or specialized operational support.
Fully Managed SOC
A fully managed model places defined monitoring responsibilities with an external SOC team. The provider operates according to an agreed scope while the healthcare organization retains responsibility for its internal systems, governance, and decisions outside the service boundary.
This model can be considered by organizations that need continuous monitoring but do not want to establish an entire SOC operation themselves.
Which Model Fits a Healthcare Organization?
There is no single answer for every healthcare organization. The appropriate model depends on internal security maturity, technical complexity, staffing capabilities, operational requirements, and the systems that require monitoring.
|
Security Model |
Potential Strength |
Key Consideration |
|
Internal SOC |
Direct operational control |
Requires sustained people, processes, and technology |
|
Co-managed SOC |
Combines internal and external capabilities |
Responsibilities must be clearly divided |
|
Fully managed SOC |
Externalizes defined monitoring functions |
Service scope and escalation procedures need careful evaluation |
The objective should be to select the model that provides appropriate security visibility while fitting the organization's operational capabilities.
Why Healthcare Needs Continuous Security Visibility
Healthcare technology environments can contain numerous interconnected systems. An organization may have clinical applications, administrative platforms, user endpoints, network infrastructure, identity systems, and other technology supporting daily operations.
A security event in one environment may become more meaningful when considered alongside activity elsewhere. SIEM capabilities can help aggregate and correlate relevant security information, while SOC analysts can investigate alerts that require human attention.
Continuous monitoring is particularly useful because security events do not follow hospital or business operating hours.
Where Traditional Monitoring Can Fall Short
Periodic security reviews can provide useful information, but they do not offer the same visibility as continuous monitoring.
An alert generated during an unattended period may remain unresolved until personnel return. Similarly, an internal IT employee responsible for several operational functions may not have the time to investigate every security event.
Automation also has limits. Security tools can identify patterns and generate alerts, but organizations still need appropriate analysis to determine what an event means in context.
A SOC helps bridge this gap by providing an operational layer between security technology and organizational response.
What to Compare When Selecting a SOC Model
Healthcare decision-makers should examine the complete operating model rather than focusing on one feature.
First, identify the systems that need monitoring. The organization should understand which security data sources can be integrated and which environments remain outside scope.
Next, examine alert handling. Ask how potentially significant events are reviewed, prioritized, investigated, and escalated.
The communication process also matters. Healthcare IT and security teams should know who receives escalations, what information is provided, and what actions require internal approval.
Finally, consider reporting and operational visibility. Regular reporting can help security leaders understand recurring alert patterns, monitoring activity, and areas requiring attention.
A Healthcare Example: Suspicious Access Activity
Imagine a healthcare organization detects unusual access activity involving a user account. Looking at the authentication event alone may not provide enough context.
A SIEM can bring together related security information from supported systems. SOC analysts can review the broader activity and determine whether the behavior appears legitimate or requires escalation.
If additional indicators suggest that the account may have been compromised, the event can be handled according to established incident procedures.
The important point is that the monitoring model provides a structured process for examining the event rather than leaving the organization dependent on a single alert.
Practical Evaluation Checklist
Healthcare organizations assessing a 24×7 SOC arrangement should consider:
- Identify the systems and security sources that require continuous monitoring.
- Define which events should receive priority.
- Confirm how analysts investigate potentially suspicious activity.
- Establish clear escalation contacts and procedures.
- Understand internal versus external responsibilities.
- Review how security data is handled within the agreed service scope.
- Confirm what reporting and operational information is available.
- Determine how changes to the technology environment will be incorporated.
- Align monitoring processes with internal security policies.
- Review the service periodically as technology and security requirements evolve.
Healthcare Compliance Context in India
Security monitoring should form part of a healthcare organization's broader information-security and data-protection approach. Organizations handling sensitive information need appropriate controls for protecting systems and information and for managing security incidents.
Where ISO 27001 is used as part of an organization's information-security framework, monitoring and incident-management activities can contribute to the wider security management process.
Healthcare organizations should also assess the specific legal, regulatory, contractual, and organizational obligations applicable to their operations rather than assuming that a SOC service alone establishes compliance.
Choosing Security Operations That Match the Environment
The best SOC model is not necessarily the largest or most automated one. It is the model that aligns monitoring coverage, analyst capability, internal responsibilities, escalation procedures, and organizational requirements.
For healthcare organizations in India, continuous monitoring can help create a more consistent approach to security visibility across supported technology environments. IBN Technologies offers cybersecurity capabilities including SIEM & SOC services that can support organizations seeking structured security monitoring and operational oversight.
When siem monitored 24x7 by a soc is evaluated as an operating model rather than merely a technology purchase, healthcare leaders can make better decisions about monitoring coverage, security responsibilities, and the level of operational support their organization actually needs.
Contact Us:
IND- 02067680404
IBN Technologies Ltd.
E-mail: - sales@ibntech.com
 Spanish
 English
 Arabic
 French
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)
 Greek